檔案類型偵測
利用OPSWAT的 AI 增強檔案類型偵測功能,防止偽造或偽裝檔案。確保超越副檔名和標頭的精確、安全
分類。
- 精確檢測
- 防止欺騙
- 更快的分流
OPSWAT 獲得以下機構的信賴
99%+ 準確度
在幾毫秒內偵測偽造檔案
類型
AI 增強型
內嵌執行
,不會造成
效能損失
涵蓋
上傳、電子郵件、
傳輸、儲存
檔案工作流程
檔案類型偵測為何重要
攻擊者偽裝檔案以繞過防禦。傳統的驗證會遺漏這些威脅,讓組織暴露在外。
偽造檔案類型
攻擊者偽裝檔案以繞過防禦。傳統的驗證會遺漏這些威脅,讓組織暴露在外。
遺漏的威脅
單靠驗證可能會遺漏隱藏的可執行程式或內嵌指令碼,讓安全團隊對危險的有效負載視若無睹。
低效率的工作流程
誤判和不完整的分類會導致掃描速度減慢、分析師無所適從,並增加作業成本。
OPSWAT 如何阻止檔案偽造
AI 增強偵測可分析結構和內容,以辨識檔案的真正類型,消除傳統驗證留下的漏洞。
內容感知偵測
超越擴展範圍,檢查結構和位元組,確保準確分類。
AI 增強精確度
機器學習可減少誤判,並改善對攻擊者經常偽裝的邊緣檔案的偵測。
無縫執行
在上傳、電子郵件或傳輸點進行線上部署,不會減慢使用者的工作流程。
檔案類型偵測如何運作
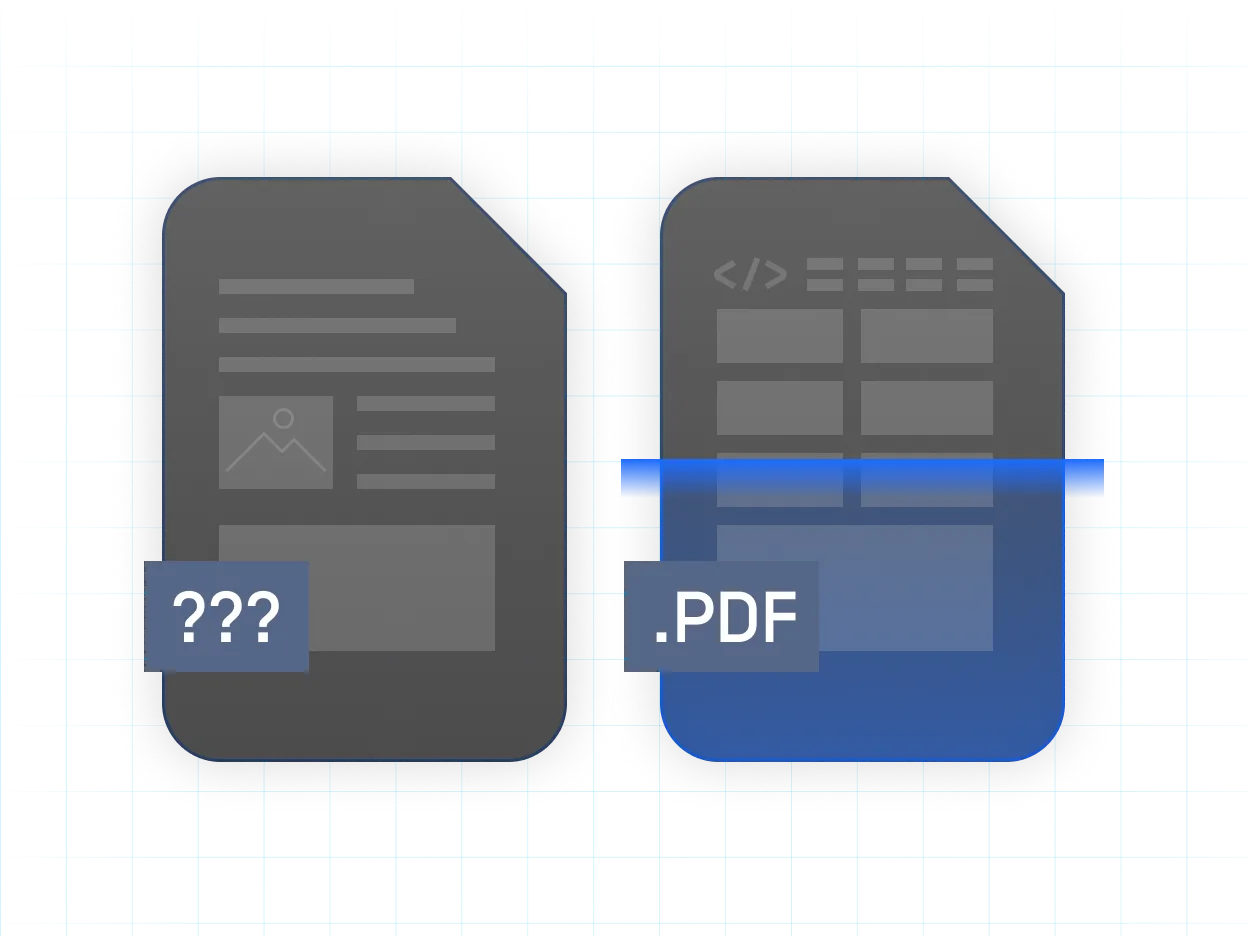
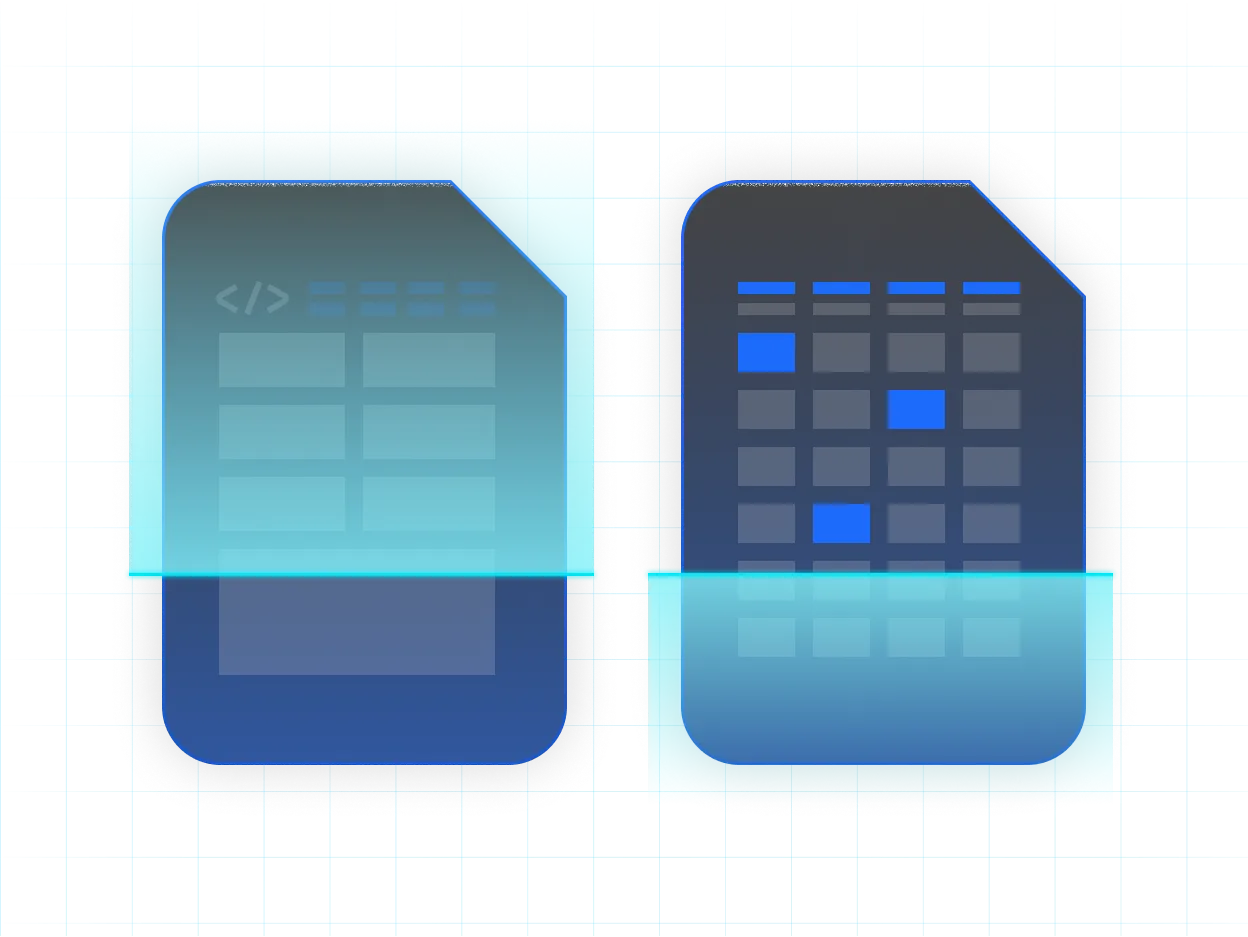
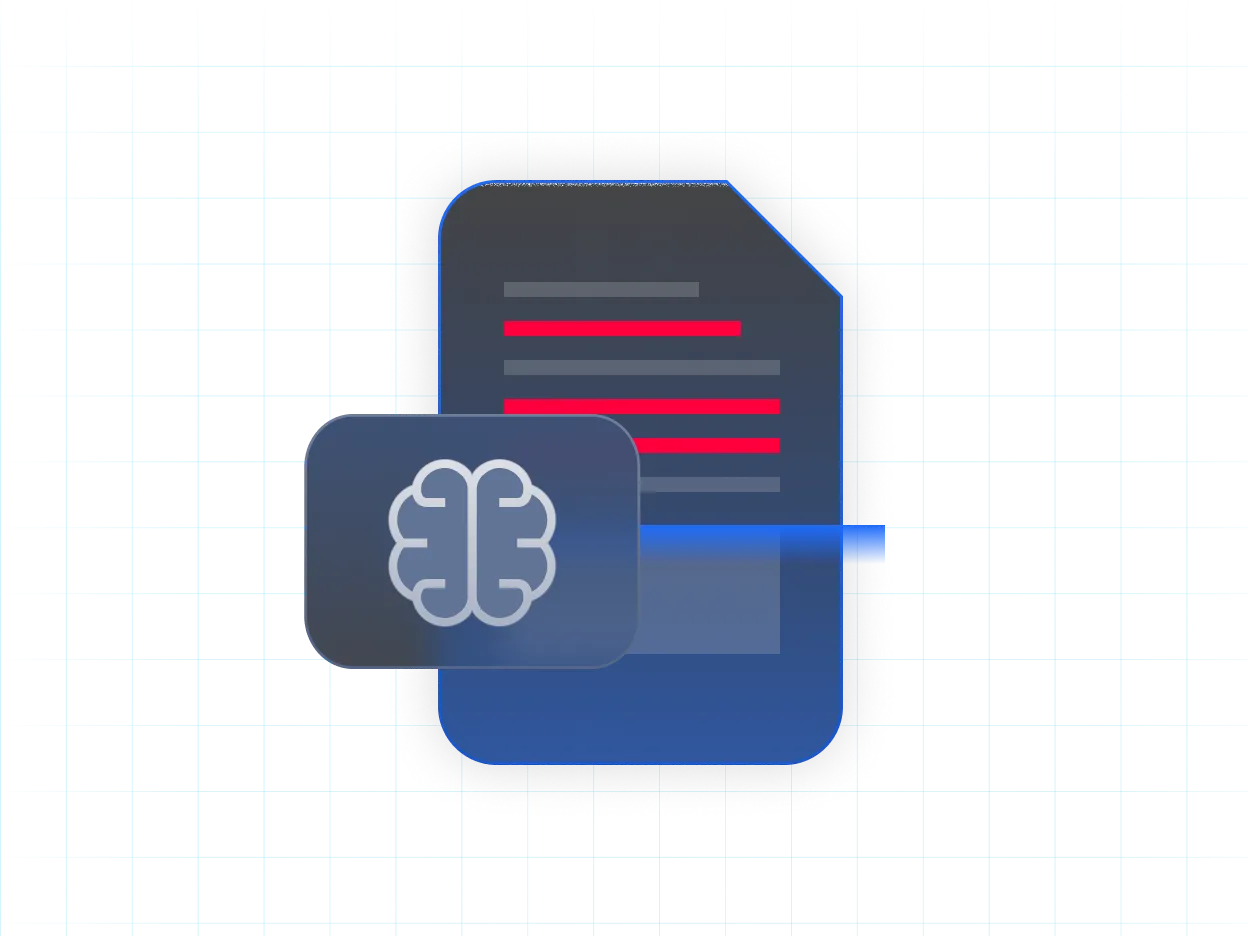
多層次的引擎結合了人工智能與經過驗證的解析和簽章檢查,提供精確的真實類型結果。

智慧型預先檢查
交叉檢查擴充套件和 MIME 標頭,以便在深入檢查前快速標示不匹配的項目。
解析器與簽章分析
針對已知的檔案類型,使用格式感知解析器和位元組層級簽章來驗證結構。AI 增強分類
應用針對文字型檔案最佳化的 AI 模型,以更高的精確度偵測偽裝或偽冒內容。
Core 優點
真正的檔案類型偵測
透過識別檔案的真正格式 - 不只是副檔名 - 防止偽造、錯誤標籤或內嵌威脅溜過。
減少誤報
AI 增強的精確度可將不必要的隔離降至最低,提高 SOC 團隊和下游安全工具的效率。
合規支援
信心十足地執行政策,確保只有經過核准的檔案類型才能進入受監管的環境,並符合稽核要求。
行動中的檔案類型偵測
File type analysis is the critical first step in securing files, identifying true file types, detecting mismatches, and enforcing policies, so every file is routed to the right security checks before entering the network.
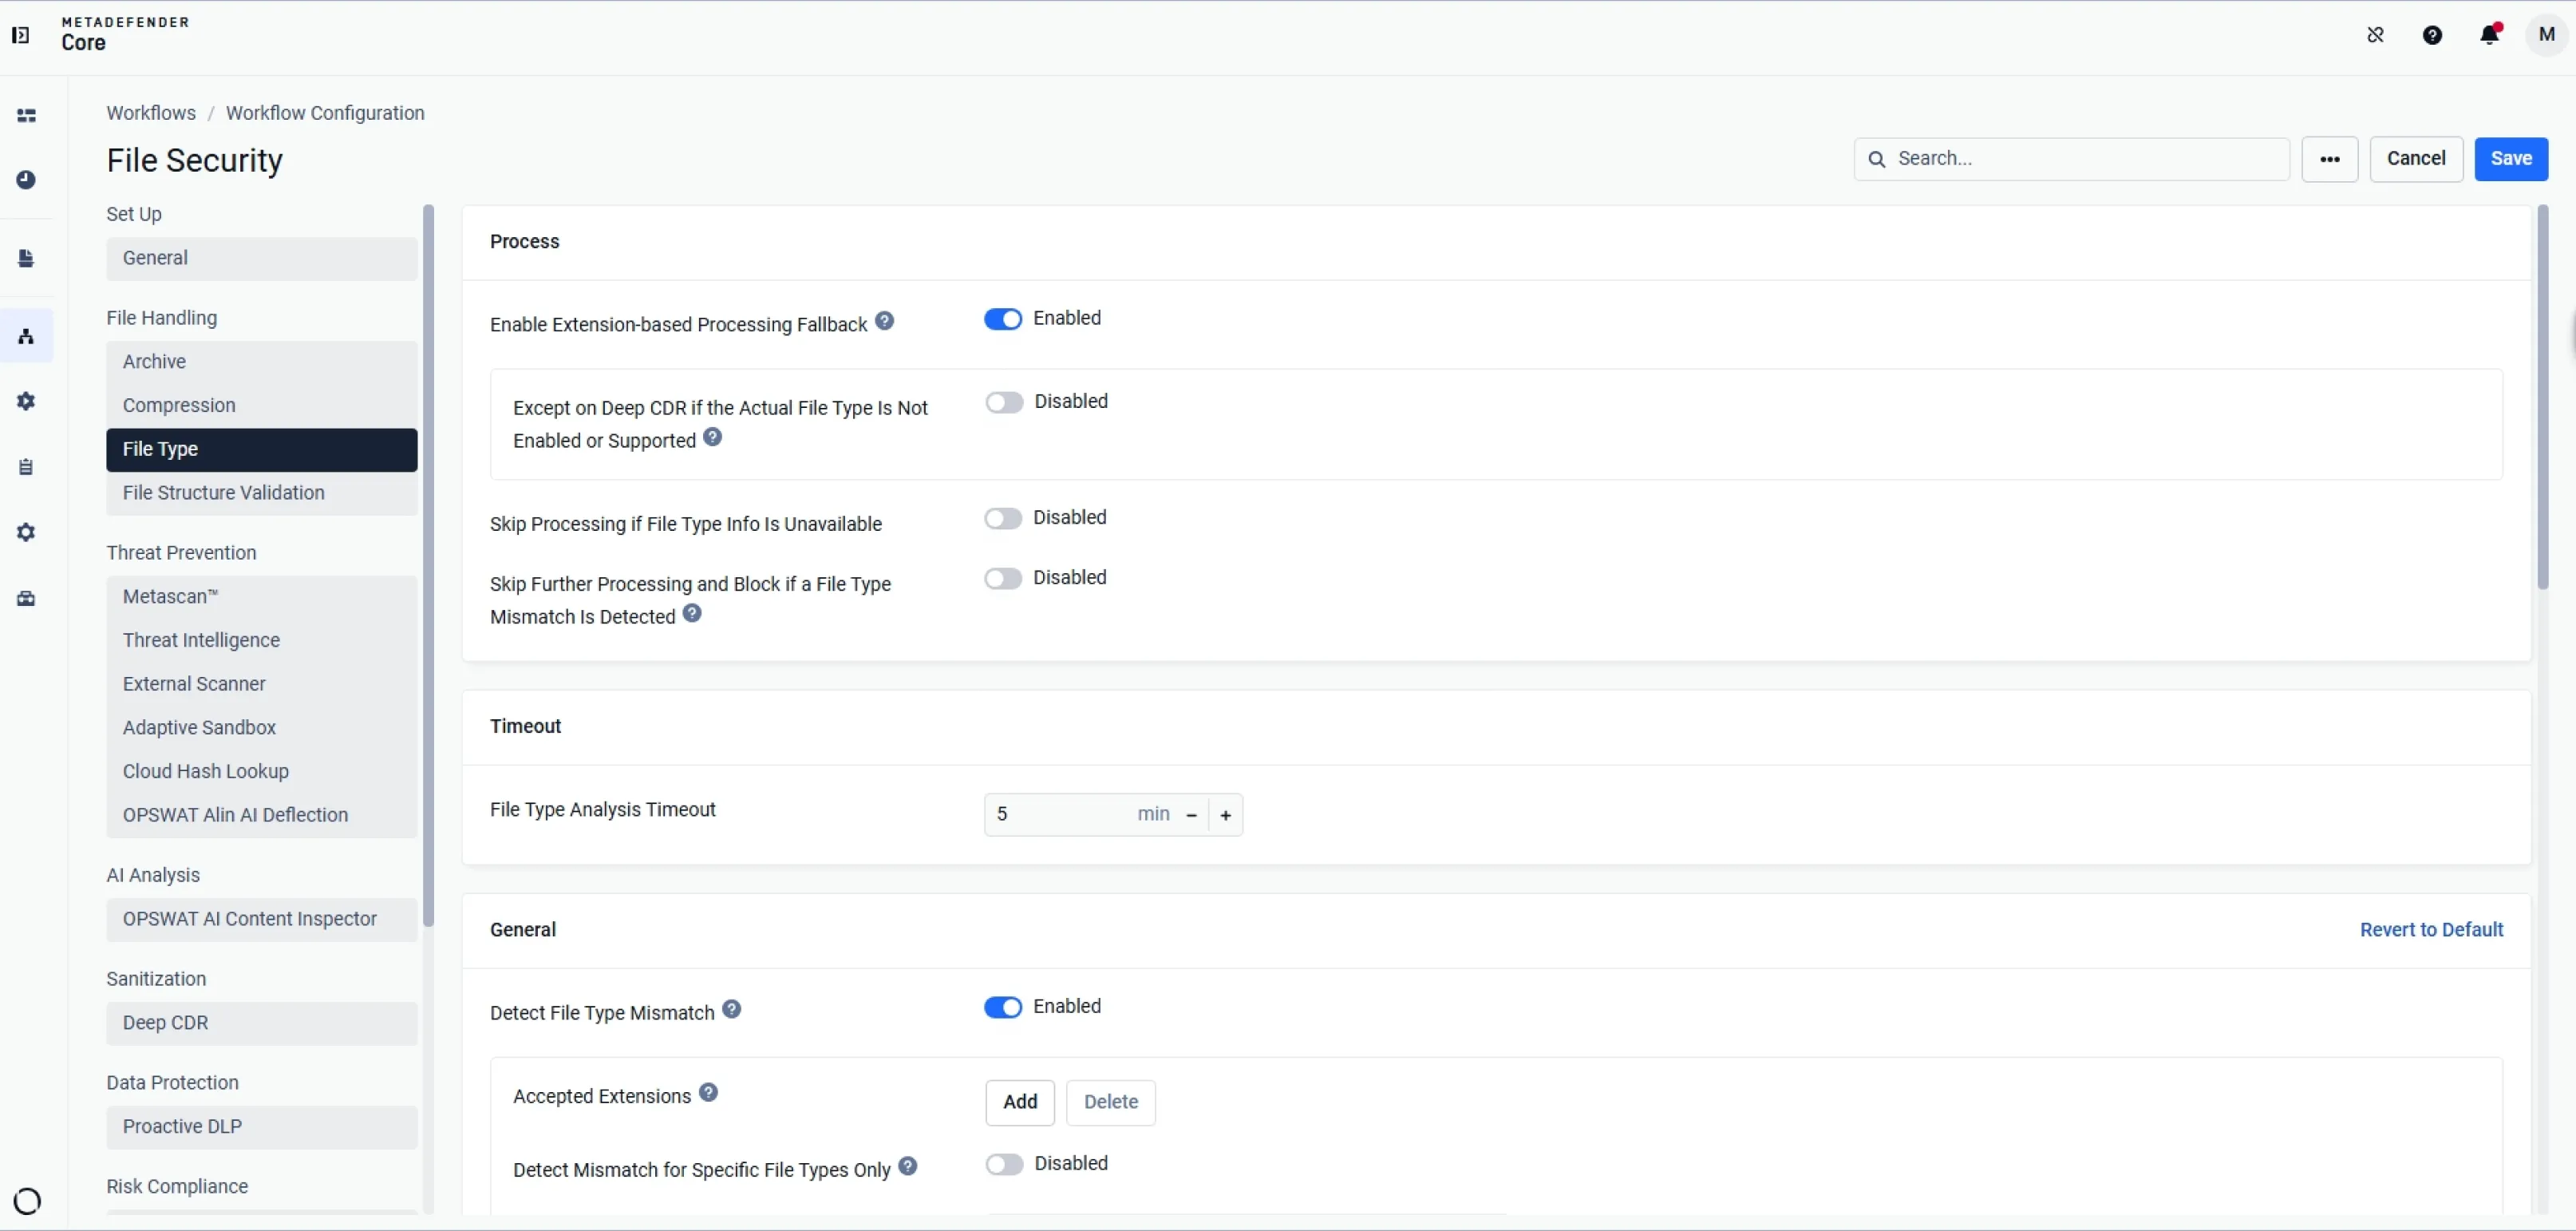
Among the first steps in the file processing workflow, Identifies true file type of an uploaded file.
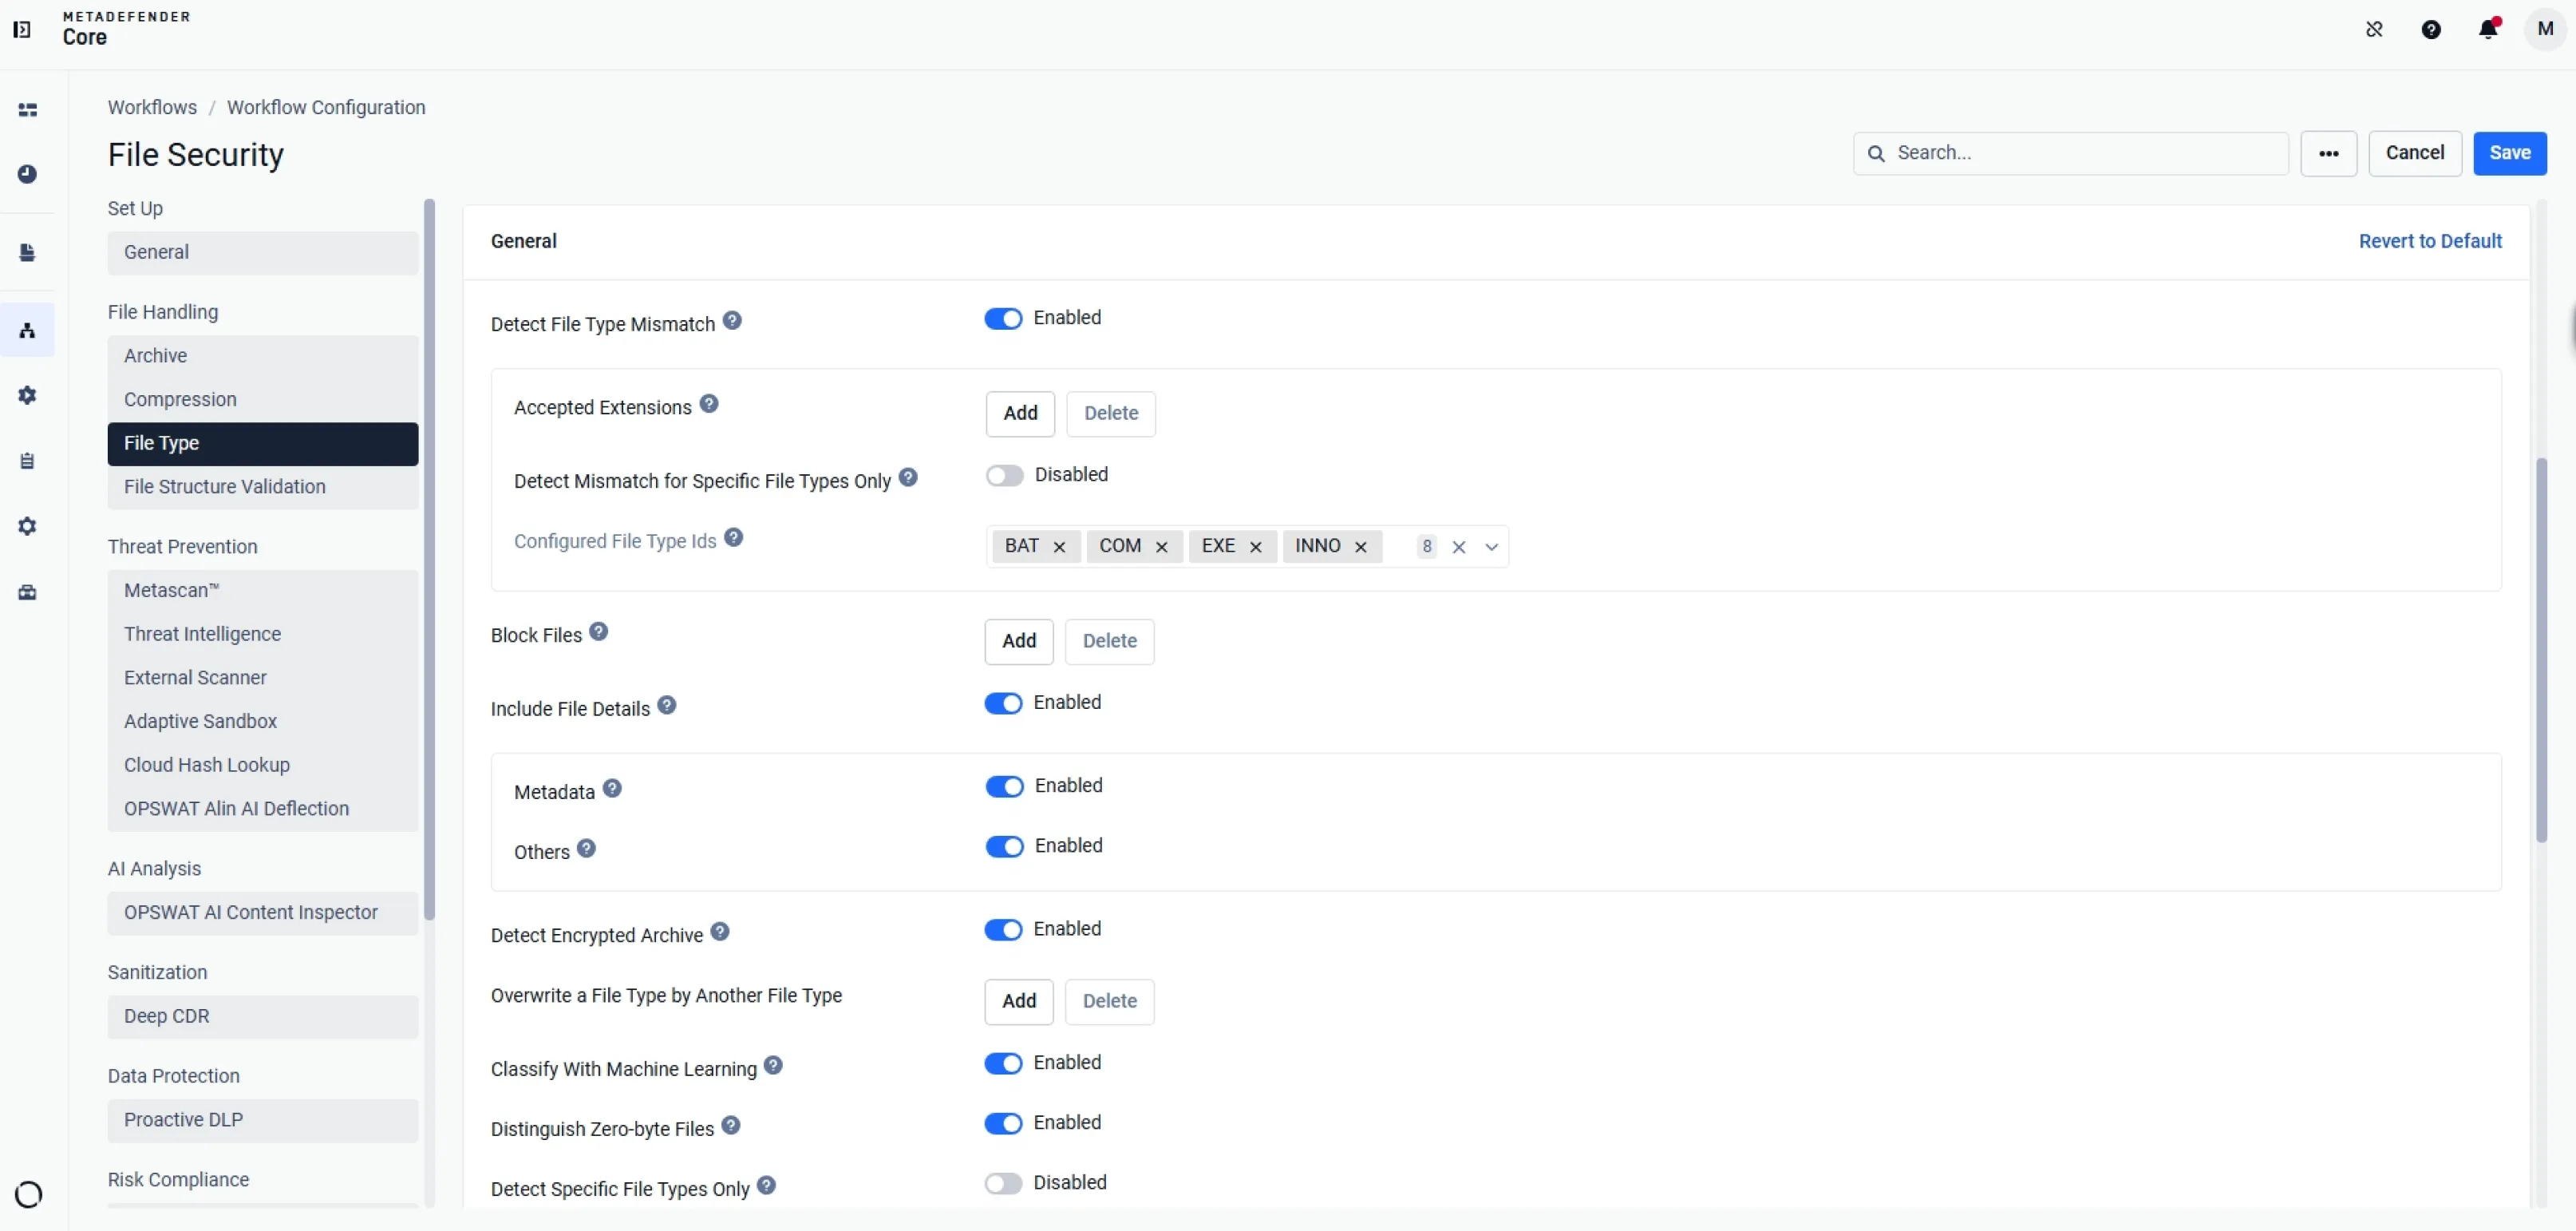
Detects file type mismatch, encrypted archive and enables text-based classification with OPSWAT Machine Learning model.
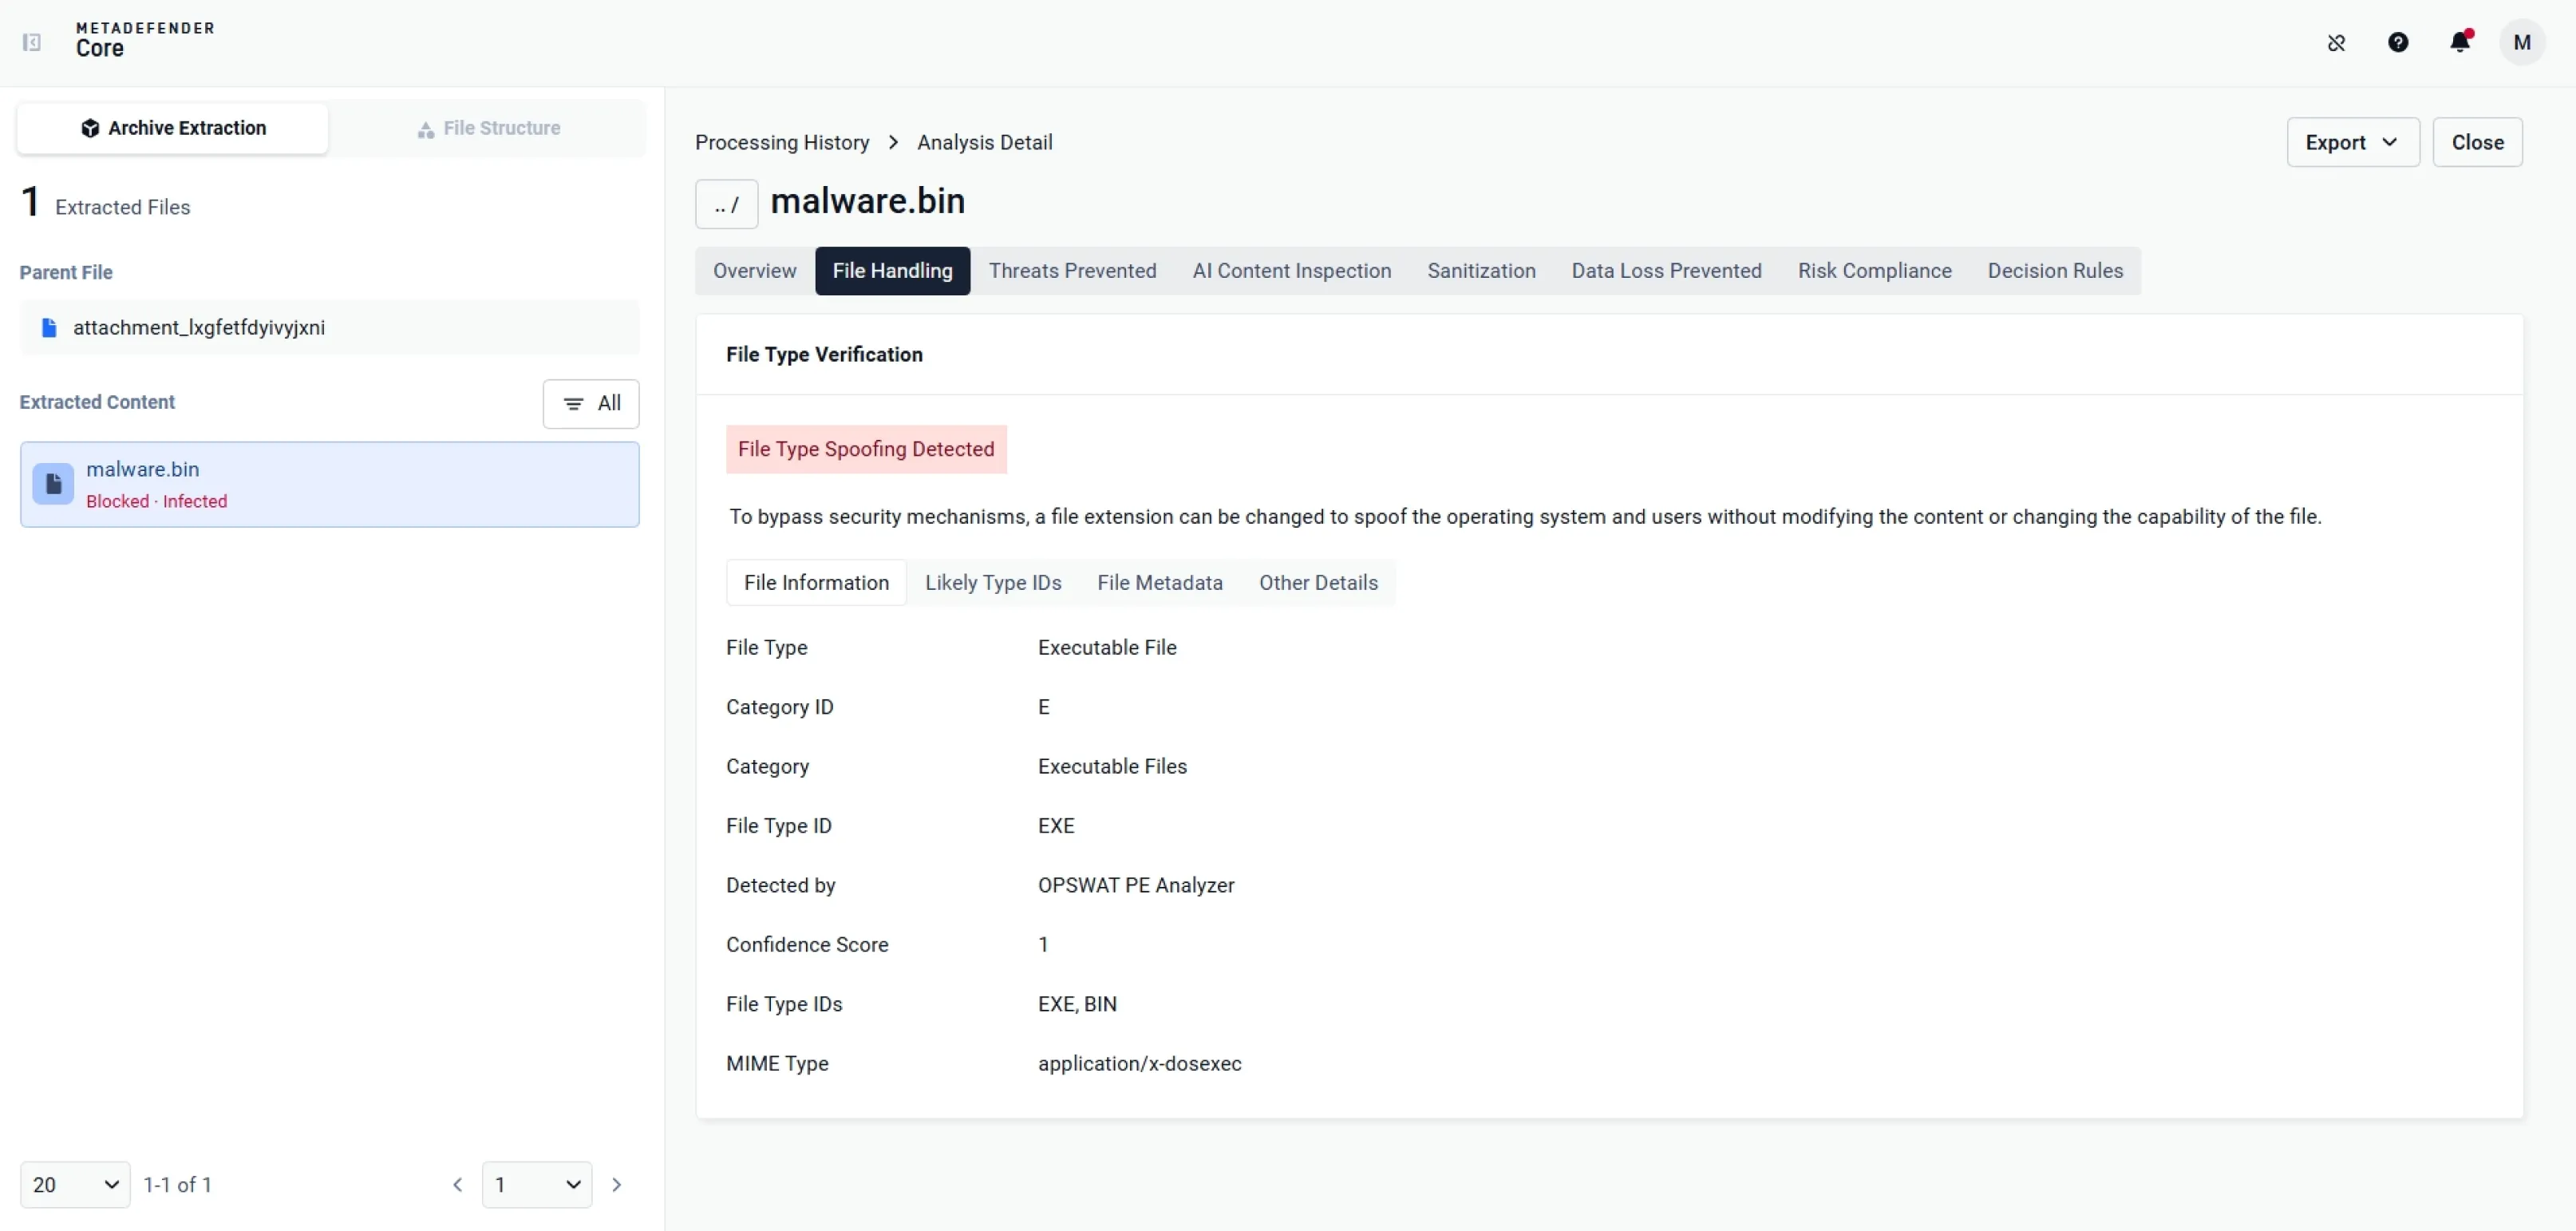
Detects file type spoofing with detailed file information including file type, category, MIME type.
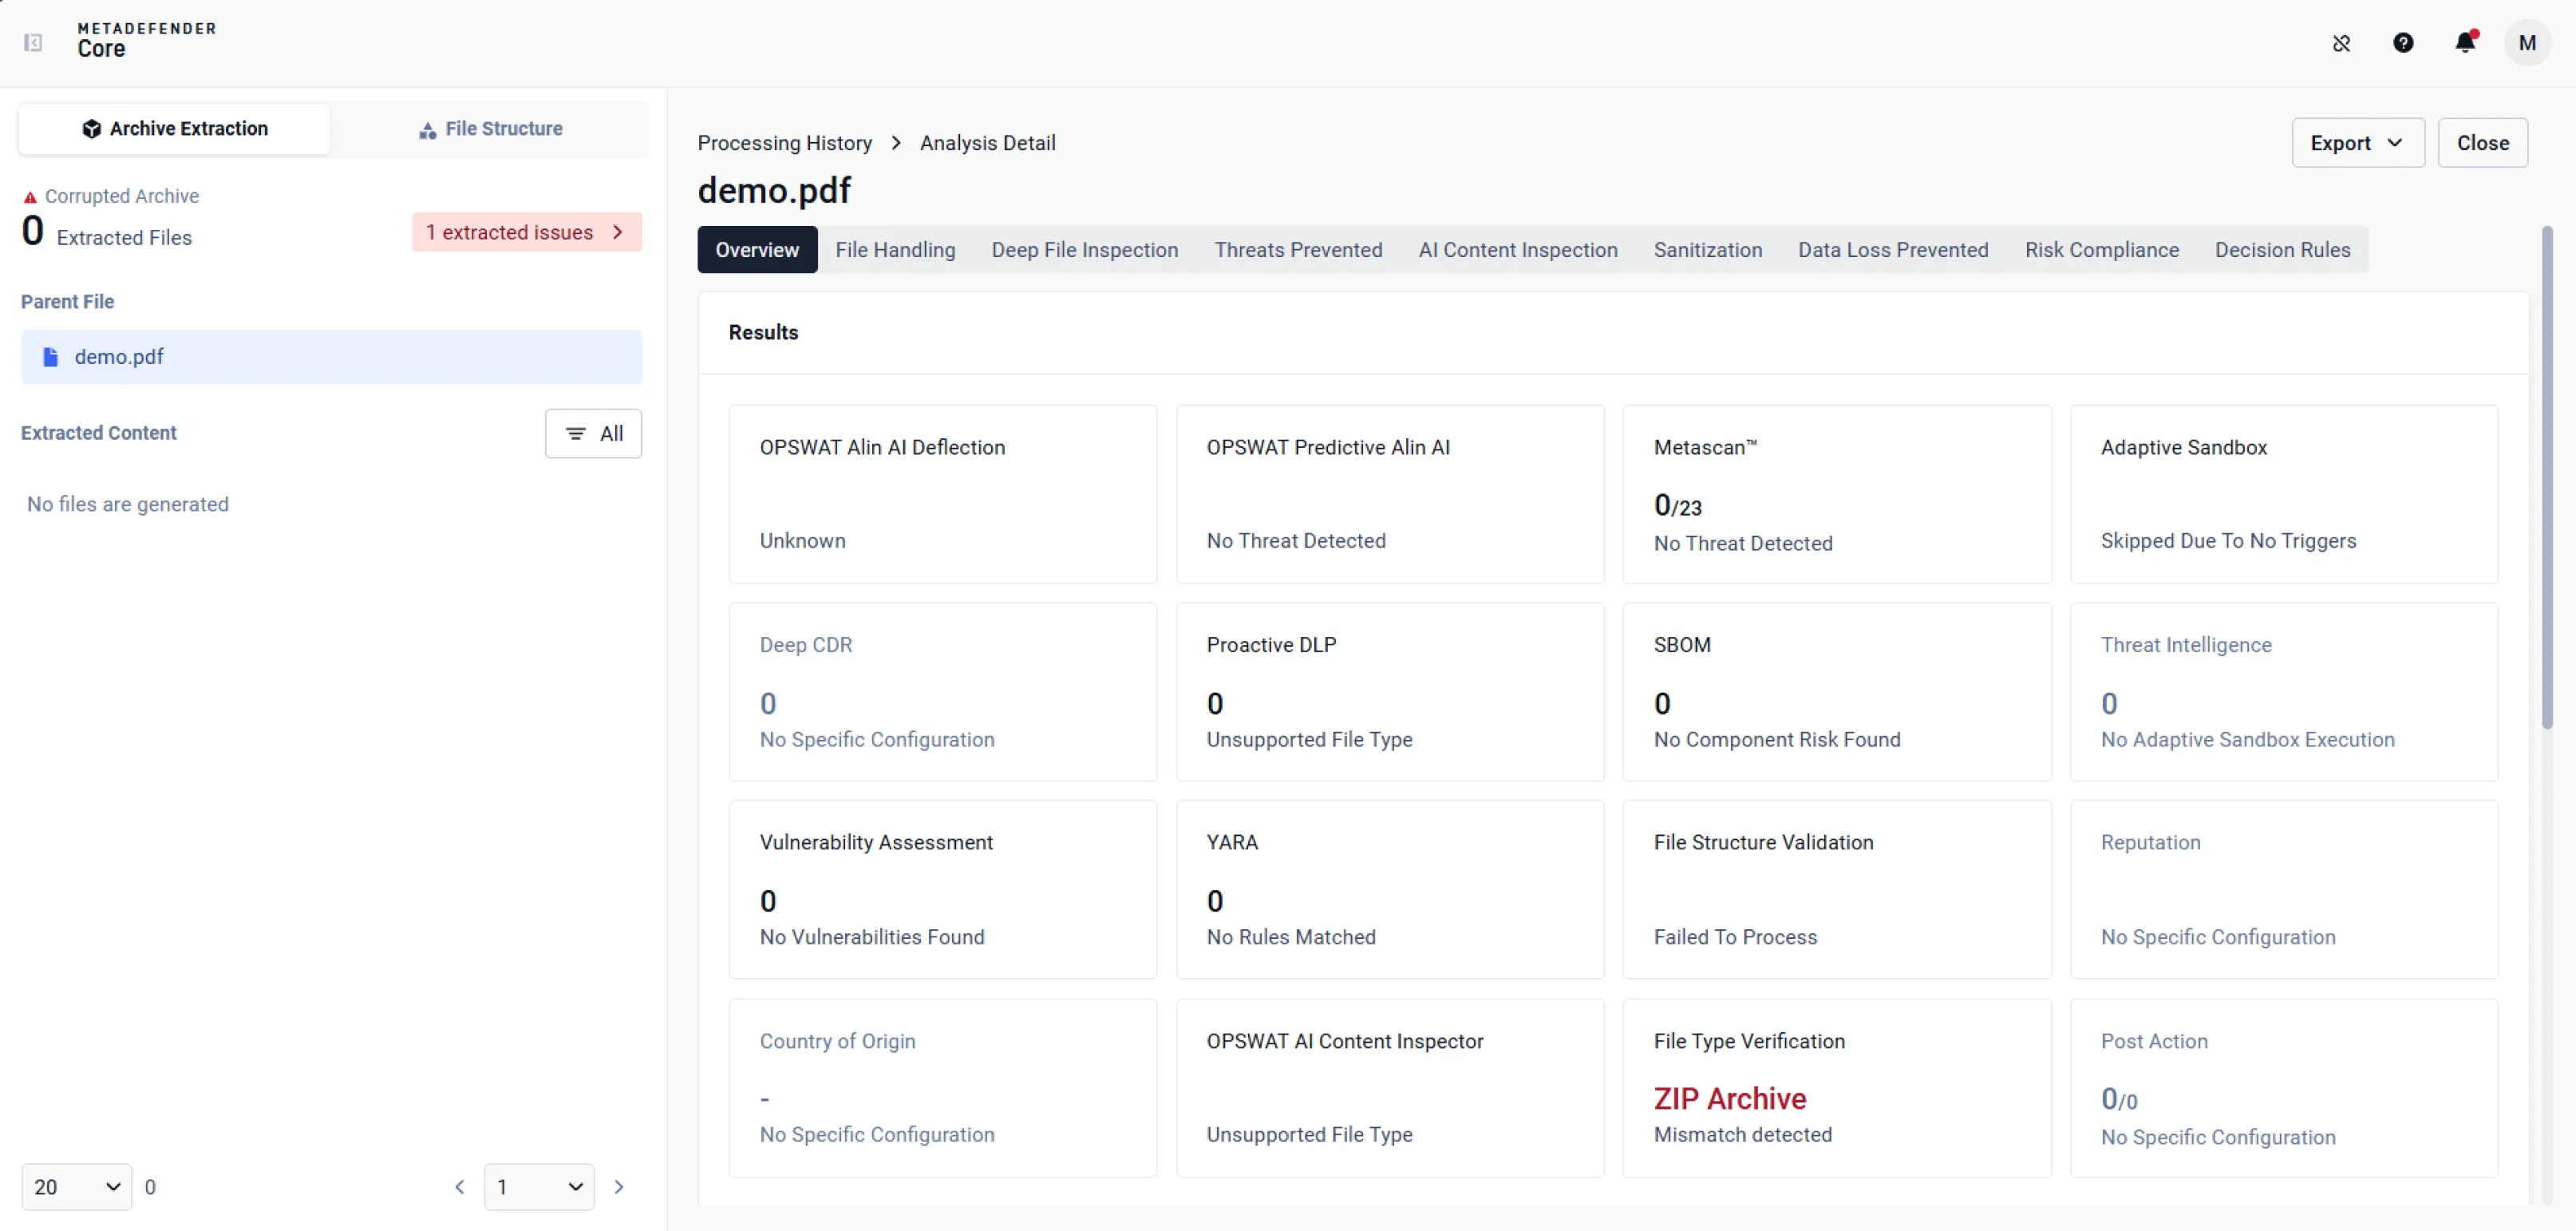
Detects and analyzes files to reveal their true type, even when disguised by misleading extensions.
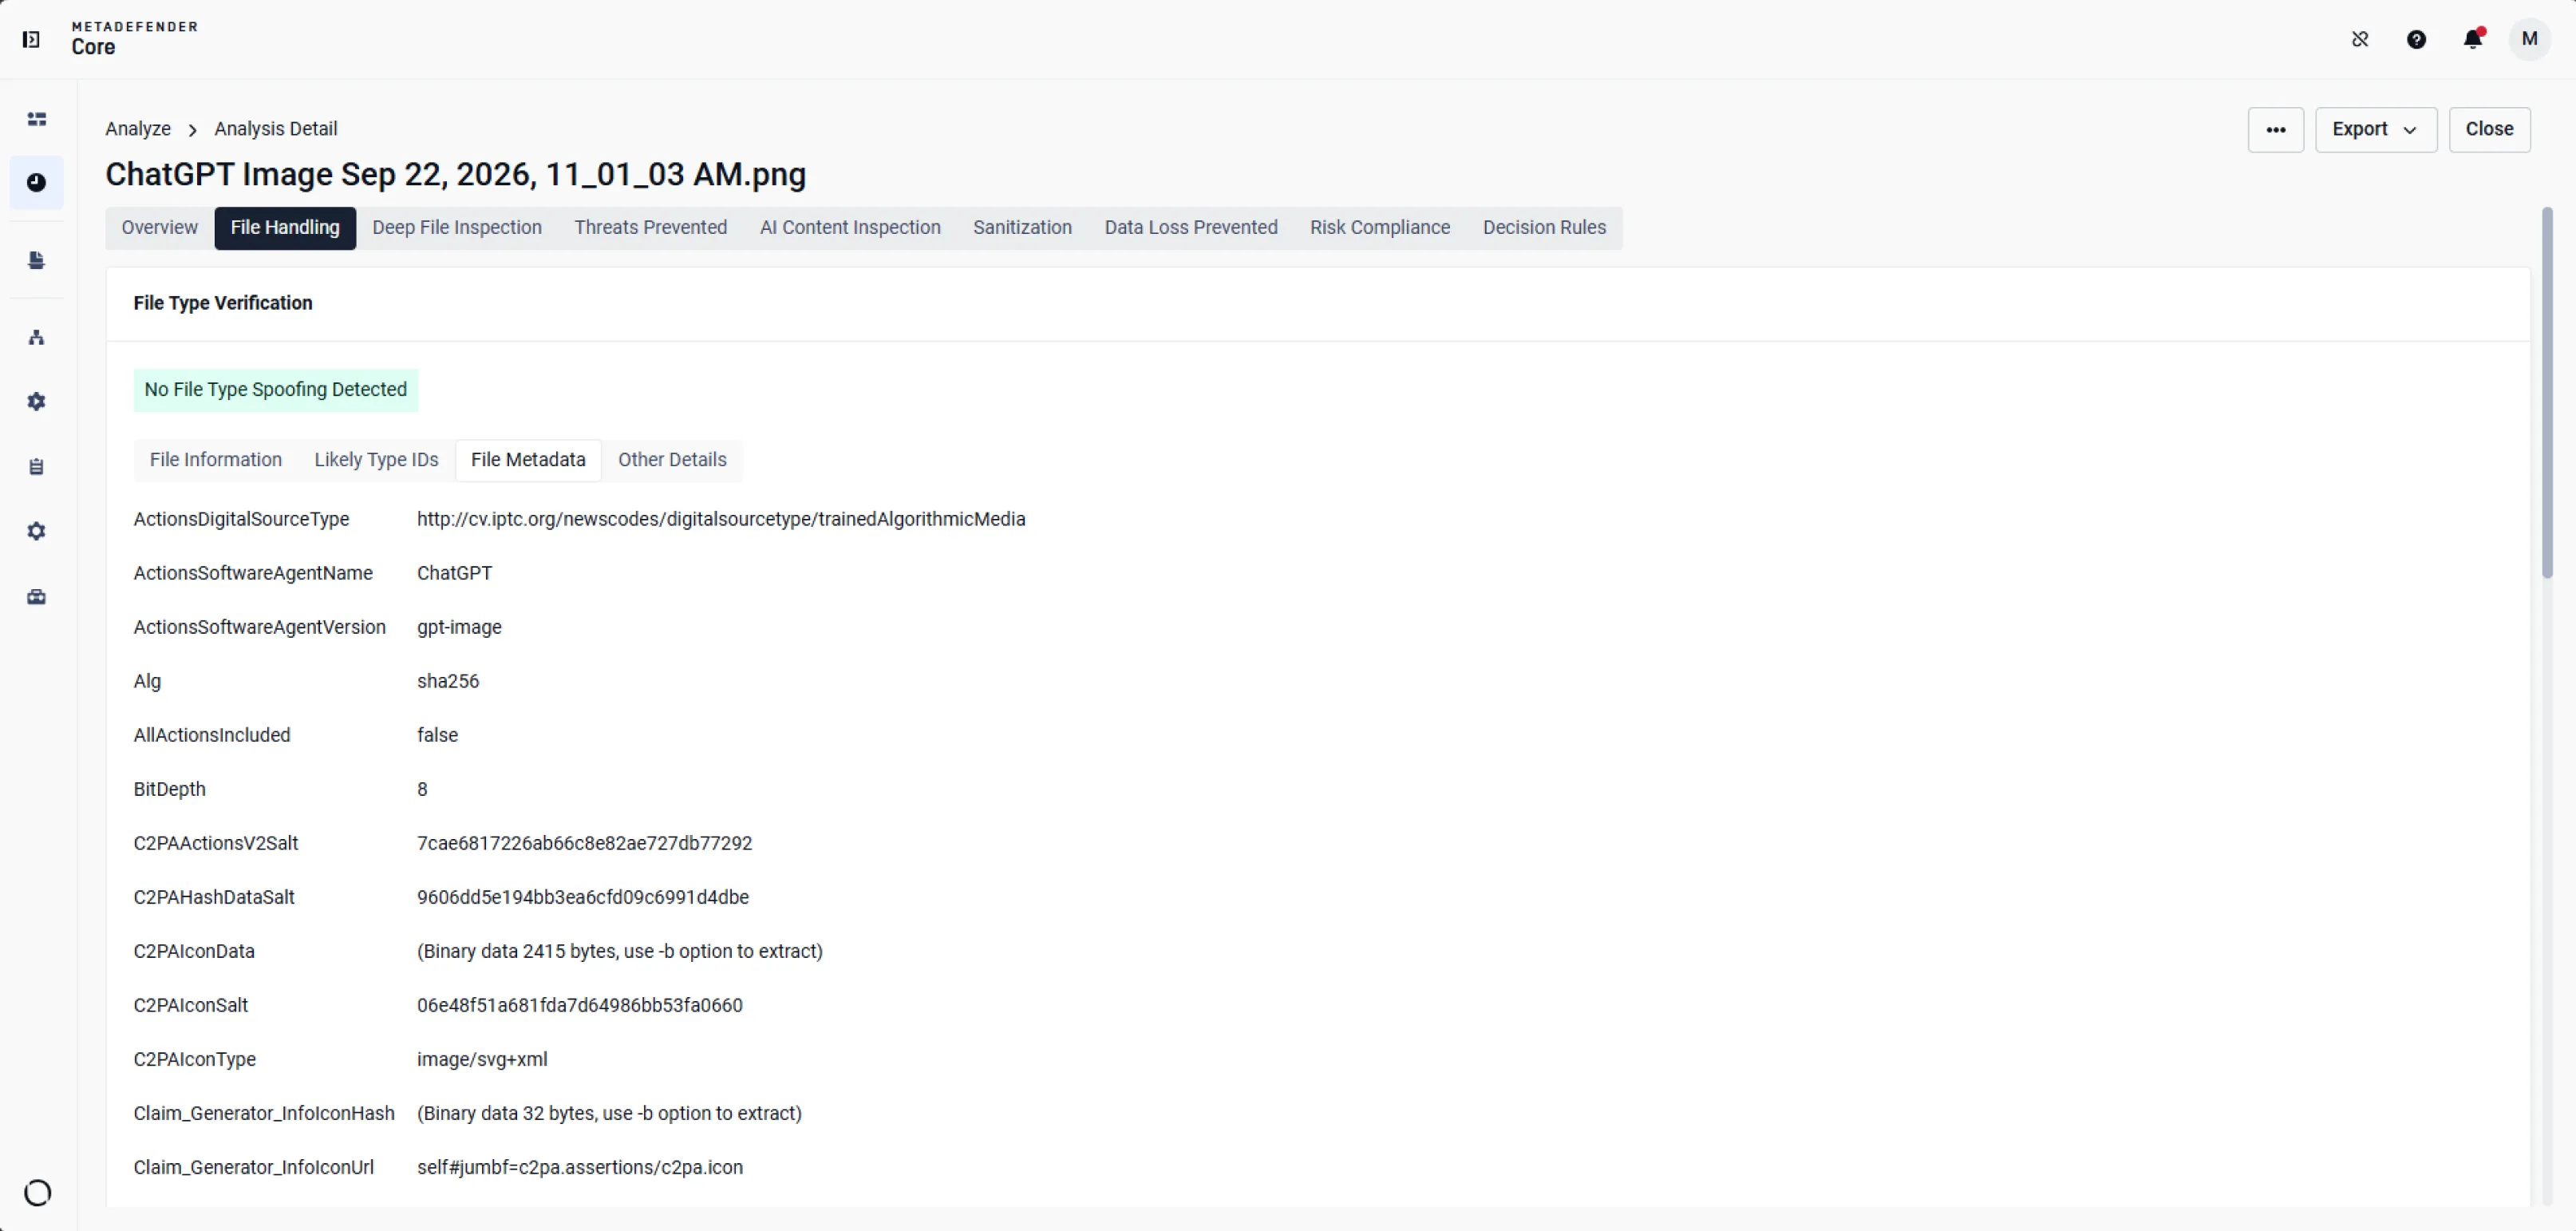
Display and extract metadata embedded in various uploaded files such as images, videos, audio files, MS Office documents, PDFs, and others.
 File Type Detection
Among the first steps in the file processing workflow, Identifies true file type of an uploaded file.
- 檔案類型偵測
Detects file type mismatch, encrypted archive and enables text-based classification with OPSWAT Machine Learning model.
- File Type Detection
Detects file type spoofing with detailed file information including file type, category, MIME type.
- 檔案類型偵測
Detects and analyzes files to reveal their true type, even when disguised by misleading extensions.
- File Type Detection
Display and extract metadata embedded in various uploaded files such as images, videos, audio files, MS Office documents, PDFs, and others.
OPSWAT 多層檔案防護對比
傳統偵測
| 能力 | OPSWAT 多層檔案保護 | 傳統偵測 |
|---|---|---|
| Metascan™Multiscanning | ||
| 深度CDR™技術檔案淨化 | 部分 | |
| 主動式 DLP™ 敏感資料偵測與修正 | ||
| 檔案解壓縮 | ||
| 檔案類型偵測 | 推薦 | 部分 |
推薦的資源
MetaDefender Core 產品型錄
由 AI 提供支援的準確檔案類型檢測

AI 增強檔案類型偵測模型 v3
ISE CVE-2025-20282:防禦上傳漏洞的檔案驗證案例
0 結果。請再試一次。
